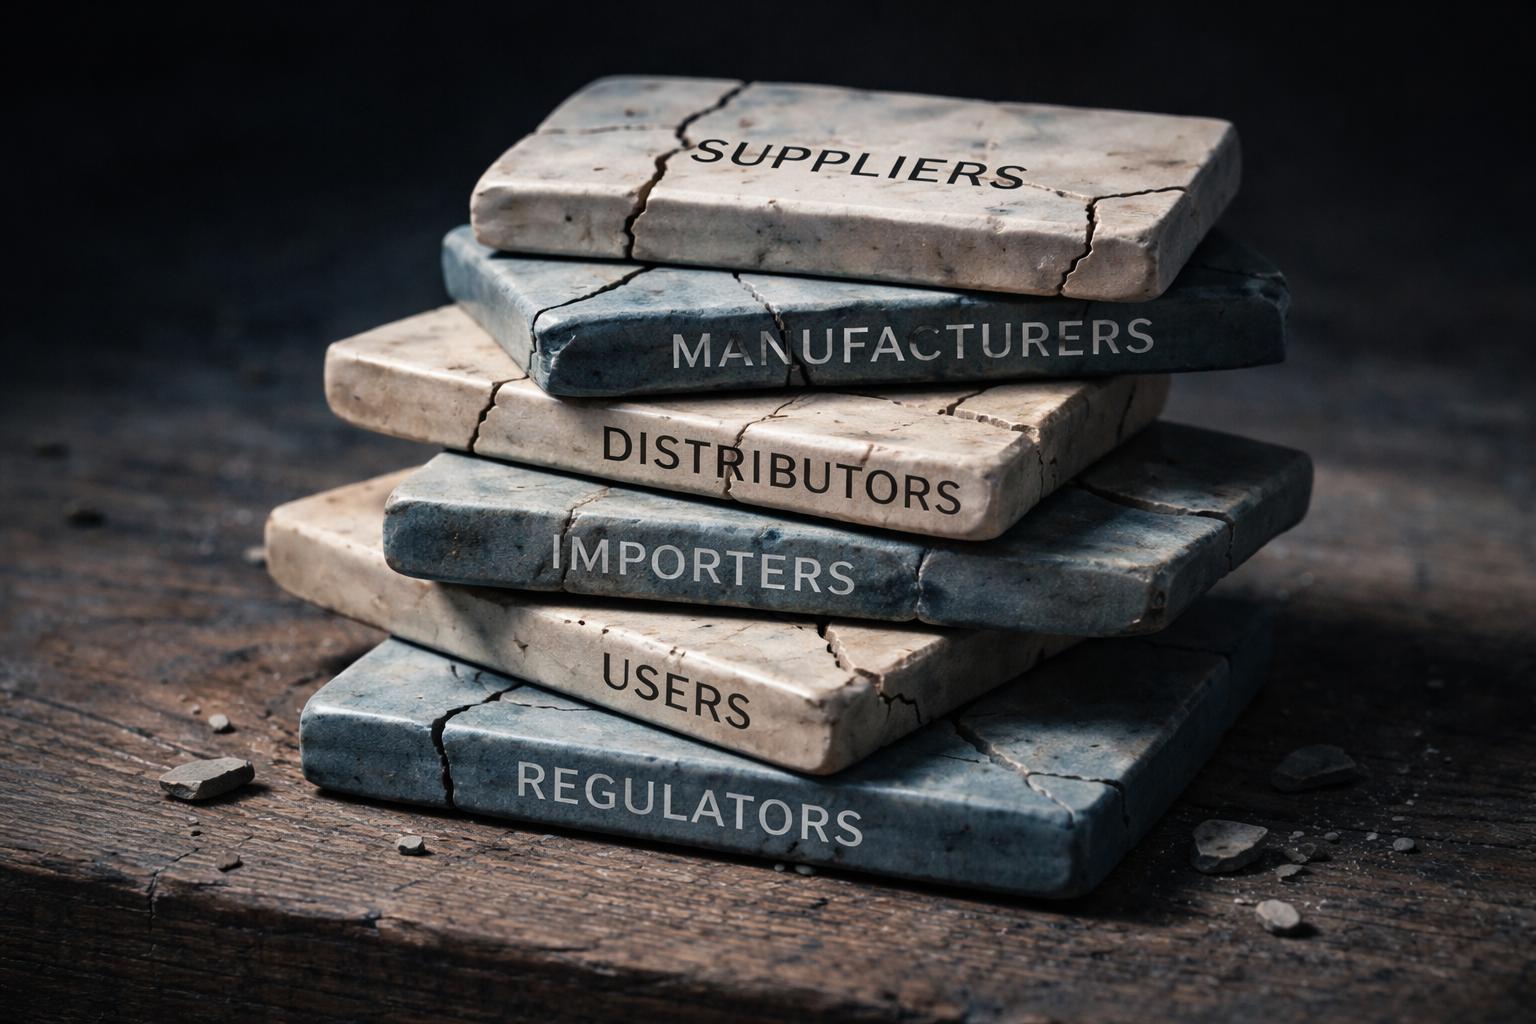
GeneralWhich CRA Role Are You? A Field Guide
The EU Cyber Resilience Act s first major deadline is September 11, 2026. If you re reading this in mid-2024 or later, you ve got about 24 months to figure out where your organization fits in the comp
Expert perspectives on application security, compliance, and emerging threats
GeneralThe EU Cyber Resilience Act s first major deadline is September 11, 2026. If you re reading this in mid-2024 or later, you ve got about 24 months to figure out where your organization fits in the comp
GeneralYour engineering team is shipping features with AI models they found on Hugging Face. Your data science group is testing LLMs through third-party APIs. Your support team just integrated a chatbot some
GeneralScope This guide focuses on identity-based security controls for AI agents that autonomously execute code, move data, and provision infrastructure. You ll learn how to implement lifecycle governance f
Your static analysis tools scanned clean. Your code review passed. Your deployment went live. And somewhere in a shopper s browser, a payment skimmer just activated from metadata hidden inside a favic
Get weekly security insights and compliance updates delivered to your inbox.
GeneralThe Conventional Wisdom Your compliance team needs an SBOM. The EU Cyber Resilience Act demands it. Executive Order 14028 requires it. Every vendor pitch deck promises that generating and managing Sof
GeneralDebian developers recently voted to encourage, but not require, disclosure of AI assistance in code contributions. The decision was to make disclosure voluntary, with mandatory human review of AI-gene
GeneralYour team just got asked to support AI agents that use Model Context Protocol (MCP). You ve got hundreds of existing APIs. Now what? This guide walks through the technical decisions you ll face when i
GeneralThe conventional wisdom: AI agents should understand user context and enforce access controls themselves. If an agent is going to retrieve data on behalf of users, it needs to know who those users are
GeneralYou ve built a fortress. Your most sensitive systems sit behind an air gap, physically isolated from the internet. No inbound connections, no outbound data leaks, no remote attacks. The compliance box
GeneralScope This guide addresses the governance gap between AI coding assistant adoption and dependency security controls. If your team uses GitHub Copilot , Amazon CodeWhisperer, or similar tools, you re a
GeneralYour compliance team just got handed another attestation framework. You re already collecting SBOMs, signing artifacts, and running policy checks across four CI/CD platforms. Now someone wants to add
GeneralThe Conventional Wisdom Your compliance program already manages non-human access. Service accounts get reviewed quarterly, API keys rotate every 90 days, and you ve got privileged access management to
GeneralYour identity management system wasn t built for entities that never log out, don t use MFA, and operate 24/7 with probabilistic reasoning. Here s what the data shows and what you need to change. What
GeneralYour security team just approved a new AI-powered code review tool. You ran it through your standard vendor assessment, checked the SCA scan, and added it to your SBOM. You re covered, right? Not even
GeneralCISA just released updates to its SBOM guidance. Your compliance team is probably updating templates right now. But here s the question: will any of this actually reduce your supply chain risk? The ho
GeneralYou download millions of packages from npm, PyPI, or Packagist each year. Your CI/CD pipeline queries these registries thousands of times per day. Your entire deployment process assumes they ll respon