The Surge in Vulnerability Discovery
In just one month, approximately 3% of all "critical" software security bugs ever recorded were discovered. This surge, driven by AI-assisted and automated vulnerability research, is a stress test for your vulnerability management program. The current pace suggests another 100,000 bugs could be found this year, challenging existing intake, triage, and patch workflows.
The Timeline of Discovery
The focus here is on the rate of discovery rather than specific dates.
- Historically: Critical vulnerabilities were discovered at a pace manageable by human researchers, allowing for predictable weekly inflow.
- Last month: AI-driven tools found about 3% of all critical software security bugs in recorded history.
- Projection: An estimated 100,000 additional bugs are expected this year.
- Your exposure window: Every new critical bug disclosure starts a clock. Attackers can exploit these vulnerabilities quickly, so your response time is crucial.
Identifying Weaknesses in Controls
When discovery volume spikes, certain controls are likely to fail. Examine these areas in your program:
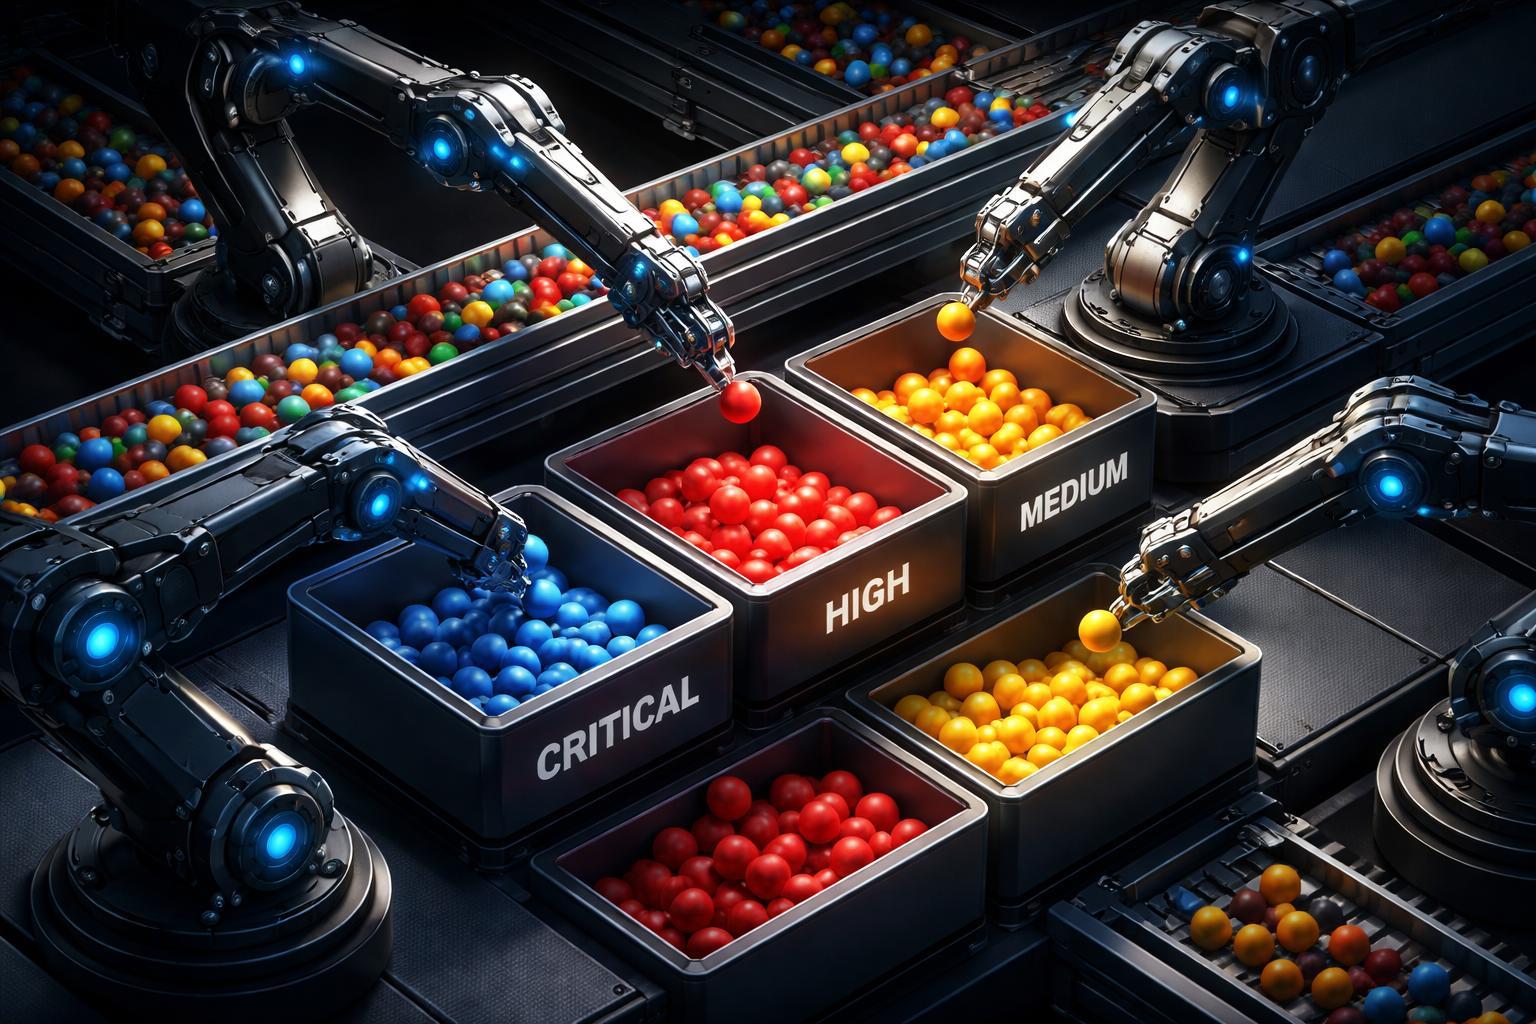
1. Prioritization based solely on severity. A rule like "fix all criticals within X days" becomes unmanageable during a surge, leading to missed SLAs or meaningless policies.
2. Manual intake and validation. Processes like manual ticket creation and CVSS review can't scale with increased inflow.
3. Incomplete asset and dependency inventory. Without a current software bill of materials, determining which of 100,000 findings are relevant is guesswork.
4. Patch pipelines sized for a steady trickle. Existing change windows and testing capacities can't handle a sudden increase in the queue.
5. Lack of compensating-control options. If "patch" is the only response, there's no plan B for unpatchable criticals.
Standards and Requirements
Frameworks don't limit the number of vulnerabilities you must handle; they require a defined, risk-based process. This is your tool when volume rises.
PCI DSS v4.0.1
- Requirement 6.3.1: Identify vulnerabilities using reputable sources and assign a risk ranking.
- Requirement 6.3.3: Install critical and high-security patches within one month of release.
- Requirement 11.3.1: Conduct internal vulnerability scans every three months, resolving high-risk vulnerabilities.
NIST Cybersecurity Framework (CSF) v2.0
- ID.RA: Identify, validate, and prioritize vulnerabilities.
- ID.AM: Asset Management underpins prioritization.
NIST 800-53 Rev 5
- RA-5 and SI-2: Scan, analyze, and remediate vulnerabilities based on risk assessment.
- Annex A control 8.8: Obtain vulnerability information, evaluate exposure, and take measures.
SOC 2 Type II
- CC7.1 and CC7.4: Maintain a consistent process for detecting and responding to vulnerabilities.
The common theme: define your process, base decisions on risk, and keep evidence of execution. None mandates immediate patching of every critical vulnerability.
Actionable Steps for Your Team
Revise your prioritization rules. Include exploitability and exposure in your criteria. Document your logic to meet PCI DSS 6.3.1 and RA-5 requirements.
Update your inventory. Maintain a software bill of materials. Quickly map new disclosures to your environment.
Automate intake and enrichment. Consolidate findings, deduplicate, and auto-tag asset ownership. Reserve analyst time for complex decisions.
Use AI defensively. Deploy AI tools to scan your code and dependencies, finding issues before others do.
Develop a compensating-control playbook. Predefine responses for unpatchable findings, such as virtual patching or network segmentation.
Re-evaluate your SLA language. Adjust SLAs based on risk to avoid repeated exceptions. Tiered SLAs are more defensible in audits.
Conduct surge rehearsals. Simulate a high volume of critical findings to identify and fix bottlenecks in your process.
The number of vulnerabilities will keep changing, but your process should ensure you remain in control.